Security
Vault and connection security
Store hosts, passwords and keys in an encrypted vault. Check which server you are connecting to and choose whether your vault needs a password to unlock.
Sign up free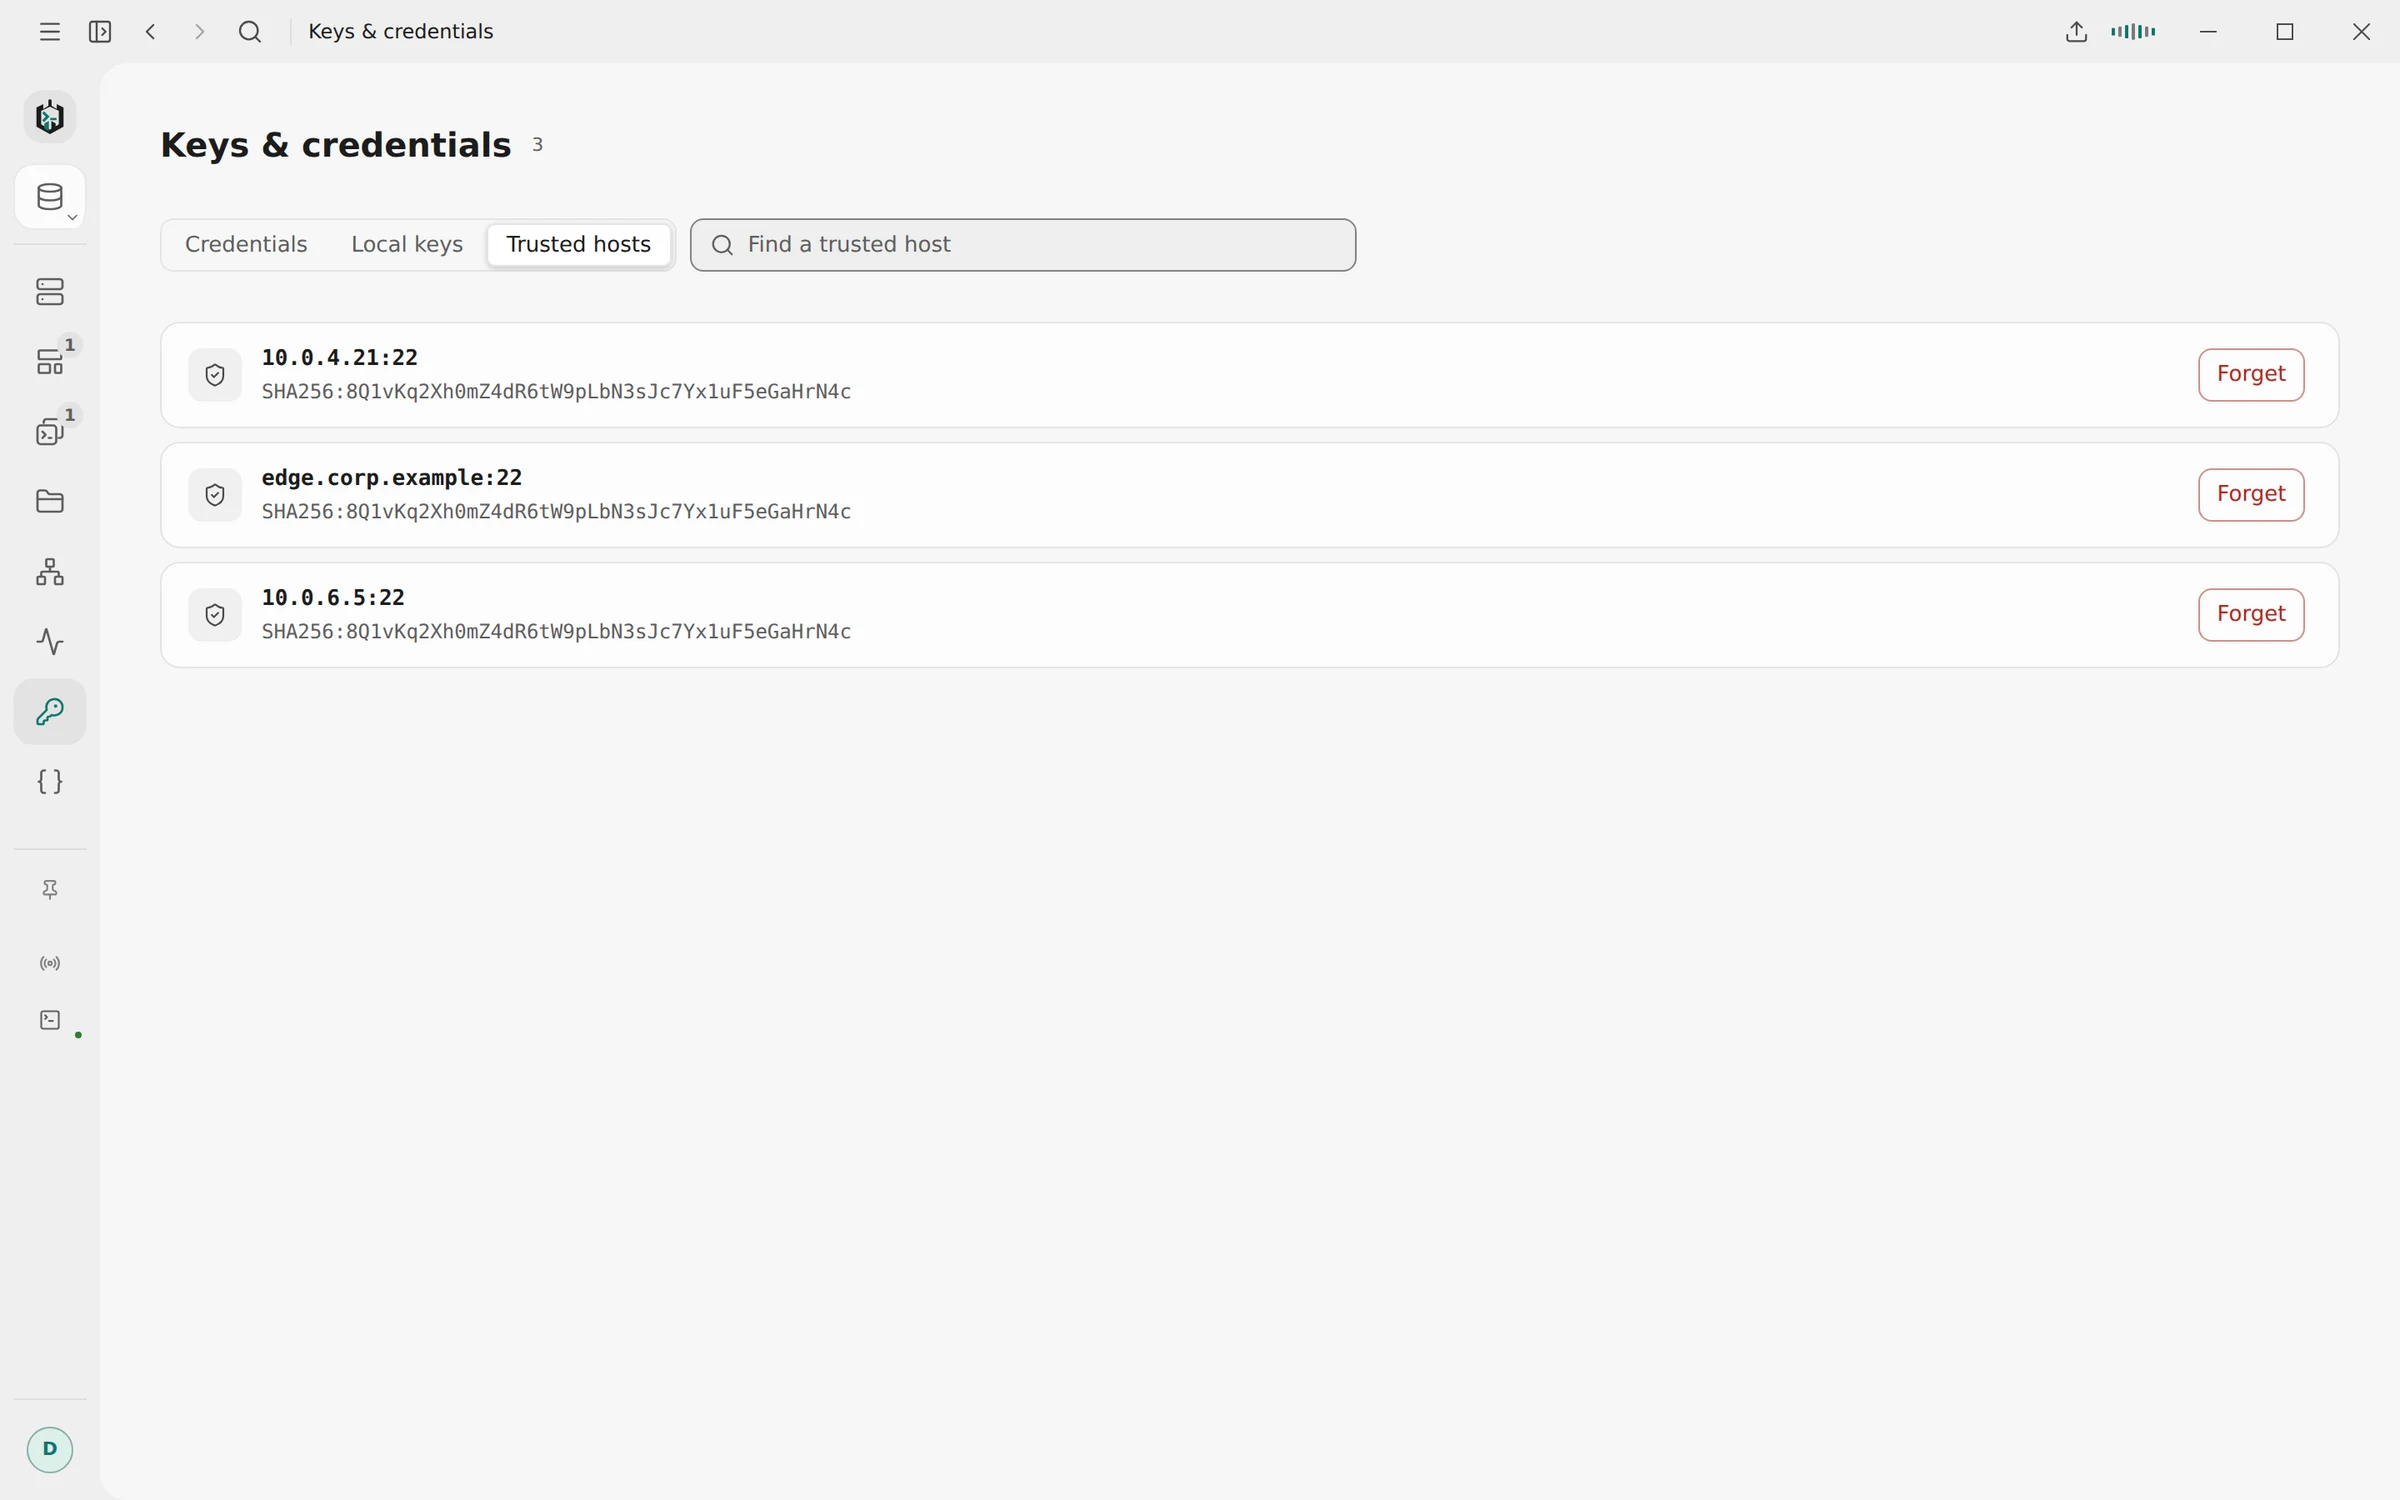
01
Vault encryption
Keep hosts, passwords, key passphrases and imported keys in an encrypted vault. The vault file is protected with AES-256-GCM encryption.
- Automatic mode: a key file beside the vault lets Ravelon open it without a password
- Encryption password lock: unlock the vault with your sync encryption password
- Master passphrase: choose a password just for this vault, without an account
- Encryption protects saved data. Ravelon can use credentials for connections while the vault is unlocked
02
Vault protection modes
Automatic mode encrypts the vault with a key file stored beside it and opens without asking. Anyone who can read both files can open the vault, including copies in a backup or synced folder. For password protection, turn on the encryption password lock or a master passphrase.
If a vault cannot be opened, Ravelon shows your recovery options. If you start over, the unreadable vault is kept beside the new one so you can still try to recover it.
“Password protection with an encryption password or master passphrase.”
03
Automatic locking
With an encryption password or master passphrase, the vault locks itself after 5 minutes to 4 hours without input, and when your computer wakes up after a longer sleep. ⌘⇧L or Ctrl+Shift+L locks it right away. Locking closes every SSH session, including its tunnels and file transfers, and every remote desktop.
- A copied team sharing key is cleared from the clipboard after 30 seconds
- Admins can cap the idle time with a policy
- Identities with passwords and keys only sync if you turn that on
04
Host key verification
Check the server key's algorithm and SHA-256 fingerprint when you first connect. Ravelon remembers the key you trust and warns you if it changes. A change may follow a server rebuild or signal an interception attempt, so check before accepting the new key.
- Verify each jump host against its own saved key
- Import trusted server keys from ~/.ssh/known_hosts
- VNC with verified TLS certificates
- RDP with TLS and Network Level Authentication
05
Diagnostics and usage data
Review connection errors in the diagnostic log without including passwords, keys, terminal input or output, or AI conversations. Usage statistics are collected only with your consent. You can review, export or delete the statistics for this installation.
The in-app updater verifies updates before installation, and you decide whether they install automatically. For Linux .deb and .rpm installations, download and install the newer package.
“Review connection errors without recording passwords, keys or terminal content.”
FAQ
Frequently asked questions
Can Ravelon read my vault?
No. The vault is encrypted on your device. With sync, the server only stores ciphertext and never gets the key.
Does Ravelon have a lock screen?
By default, Ravelon opens your hosts without a lock screen. Enable an encryption password or master passphrase to require unlocking, and choose when the vault locks after inactivity.
Are usage statistics enabled by default?
No. Ravelon asks after setup and collects usage statistics only if you agree. Change your choice in the privacy settings at any time. Administrators can also disable usage statistics through a policy.
What does the diagnostic log contain?
App starts, SSH connection steps, host key checks and errors, along with host addresses, ports, user names and fingerprints. Never passwords, keys, passphrases, terminal input or output, or AI conversations.
Get started
Try it in your own workspace.
Use the encrypted vault, terminal, SFTP and Ravelon Agent in the free desktop app. Ravelon Pro adds Cloud sync with a one-time purchase. Any AI provider charges are separate.
Related features
Vault & sync
Sync encrypted vault data between devices. Approve new devices before they use Ravelon Cloud.
SSH terminal
SSH with your passwords and keys kept in an encrypted vault.
For companies
Set company-wide rules and use your existing network settings.
Team vaults
Share encrypted vaults and choose what each team member can use or edit.